The countdown to a post-quantum internet has acquired a new instrument. Black Kite, a provider of third-party cyber risk management tools, has introduced Quantum Readiness, a control set built into the SSL/TLS Strength category of its Cyber Rating engine. The addition lets organizations see, from the outside, which vendors in their supply chains have begun adopting quantum-resistant cryptography and which still depend on algorithms regulators plan to retire.
Why cryptographic agility now matters
Modern encryption, including RSA and elliptic-curve methods such as ECDSA and ECDH, relies on mathematical problems that are extraordinarily difficult for classical computers to solve. A sufficiently powerful quantum computer, however, could in theory unravel them far faster, rendering today's "secure" connections readable in retrospect. This has given rise to the so-called "harvest now, decrypt later" threat model: adversaries intercept and store encrypted data today, betting that future quantum capability will let them decrypt it later. Data with long confidentiality requirements - financial records, health information, government communications - is especially exposed to this delayed-fuse risk, even though large-scale quantum decryption capability does not yet exist.
Post-quantum cryptography refers to new algorithms designed to resist both classical and quantum attacks, now being standardized internationally. The transition is not a single switch-flip; it involves hybrid key exchange mechanisms that combine classical and quantum-resistant methods, along with new certificate formats capable of carrying PQC-ready digital signatures. Measuring this transition has historically been difficult because much of it happens inside vendor infrastructure, invisible to the organizations that depend on them.
What the new control set actually measures
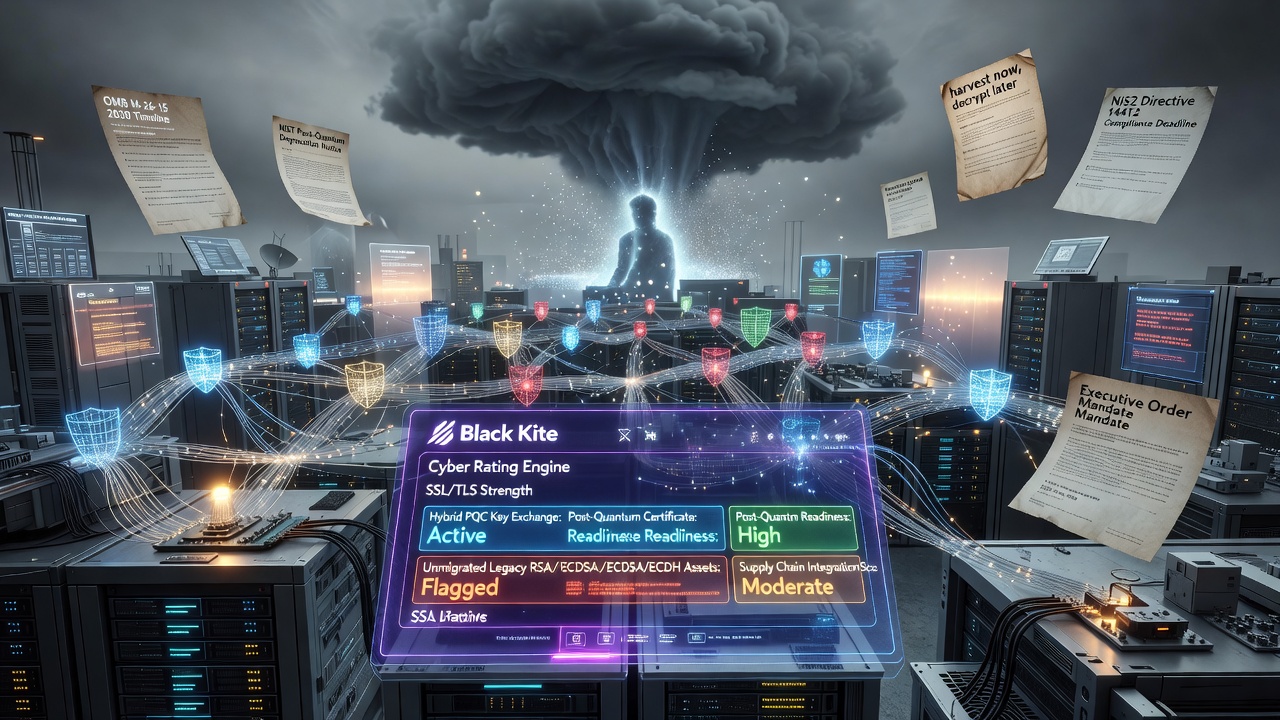
Black Kite's approach works by observing external, verifiable signals rather than requiring vendors to self-report. The assessment covers four areas: whether a vendor has deployed active hybrid PQC key exchange, whether its digital certificates show signature readiness for post-quantum standards, whether legacy assets still running RSA, ECDSA, or ECDH remain unmigrated, and how all of this factors into the broader SSL/TLS scoring already used across the platform's vendor ratings.
- Key exchange agility: detects hybrid post-quantum key establishment mechanisms in active use.
- Certificate readiness: inspects digital certificates for post-quantum signature support.
- Asset vulnerability mapping: flags legacy cryptographic assets that have not been migrated.
- Supply chain integration: folds these signals into existing third-party risk scoring.
Regulatory deadlines are driving the timeline
This is not a purely technical exercise. U.S. federal guidance under OMB memorandum M-26-15 sets a 2030 target for migrating to post-quantum key establishment, with digital signature migration expected by 2031. Executive Order 14412 pushes federal contractors toward similar timelines through procurement requirements, meaning companies selling into government supply chains will need to demonstrate cryptographic readiness contractually, not just technically. NIST's own deprecation schedule anticipates phasing out current algorithms after 2030, with full disallowance by 2035. In Europe, the NIS2 Directive imposes supply chain risk management obligations that extend cryptographic accountability to third-party relationships, with compliance expectations building through 2026 and beyond.
For organizations managing hundreds or thousands of vendor relationships, manually verifying cryptographic posture at this scale is unrealistic. Continuous, externally observable monitoring offers a way to prioritize which vendors pose the greatest exposure as deadlines approach, and to build evidence trails for auditors and regulators asking whether supply chain cryptographic risk is being actively managed rather than assumed away.
The broader stakes
Quantum computing capable of breaking current public-key cryptography does not yet exist in a form that threatens everyday encrypted traffic. But cryptographic migration across global infrastructure takes years, and the data being transmitted today may still need protection a decade from now. Tools that make vendor-level cryptographic posture visible, rather than assumed, mark a shift in how third-party risk is assessed - treating quantum readiness as a measurable security attribute rather than a distant policy abstraction.